Enterprise web security
that adapts as fast as threats do
Setting up a firewall is easy. Keeping it effective is the hard part. And the part most enterprise web security implementations get wrong.
IDO Edge combines a continuously tuned OWASP WAF, real-time attack detection via RADR, smart bot management and DDoS protection - actively managed by security experts as part of your Frontend Management Suite.
Most enterprise websites are protected by a WAF nobody maintains
Enterprise applications change constantly - new cookies, new partners, new pages, new APIs. The average enterprise app changes 52 times a week. But most WAF protection service setups don't keep pace.
Rules are set once, left untouched, and slowly become either dangerously permissive or so restrictive they break legitimate traffic.
The instinct is to switch rules off. But every rule that gets turned off is one less line of defence.
Meanwhile, 47% of web traffic is now malicious bot activity, and multi-vector attacks have grown 300% since 2020.
Enterprise web security built on static rule sets isn't a defence. It's a false sense of security.
And attackers know it.
Why enterprise web security must adapt as fast as threats do
The modern threat landscape demands security that learns, tunes and responds - not rule sets you configure once and forget.
Your WAF Is Already Out of Date
Enterprise applications change 52 times a week on average. Static WAF rules set at launch become gaps. Attackers know it - and exploit it.
Nearly Half of All Web Traffic Is Malicious
Bots, credential stuffing and volumetric abuse erode performance, distort analytics and inflate infrastructure costs - all before anyone notices.
Multi-Vector Attacks Have Tripled
Attackers don't probe one entry point. Modern threats combine DDoS, credential abuse and injection simultaneously - requiring equally adaptive defence.
Security Needs to Adapt as You Change
IDO Edge actively profiles your application and tunes WAF rules over time - so protection strengthens with every release, not weakens.
IDO Edge brings protection, visibility and speed together
So your teams can ship confidently without compromising security
Enterprise web security that earns its keep
IDO Edge doesn't just install a WAF and walk away. Every deployment is actively managed by security experts who profile your application, mine WAF events into tuning proposals and respond when threats emerge.
It's enterprise web security that gets more precise over time, because the right people are always watching.
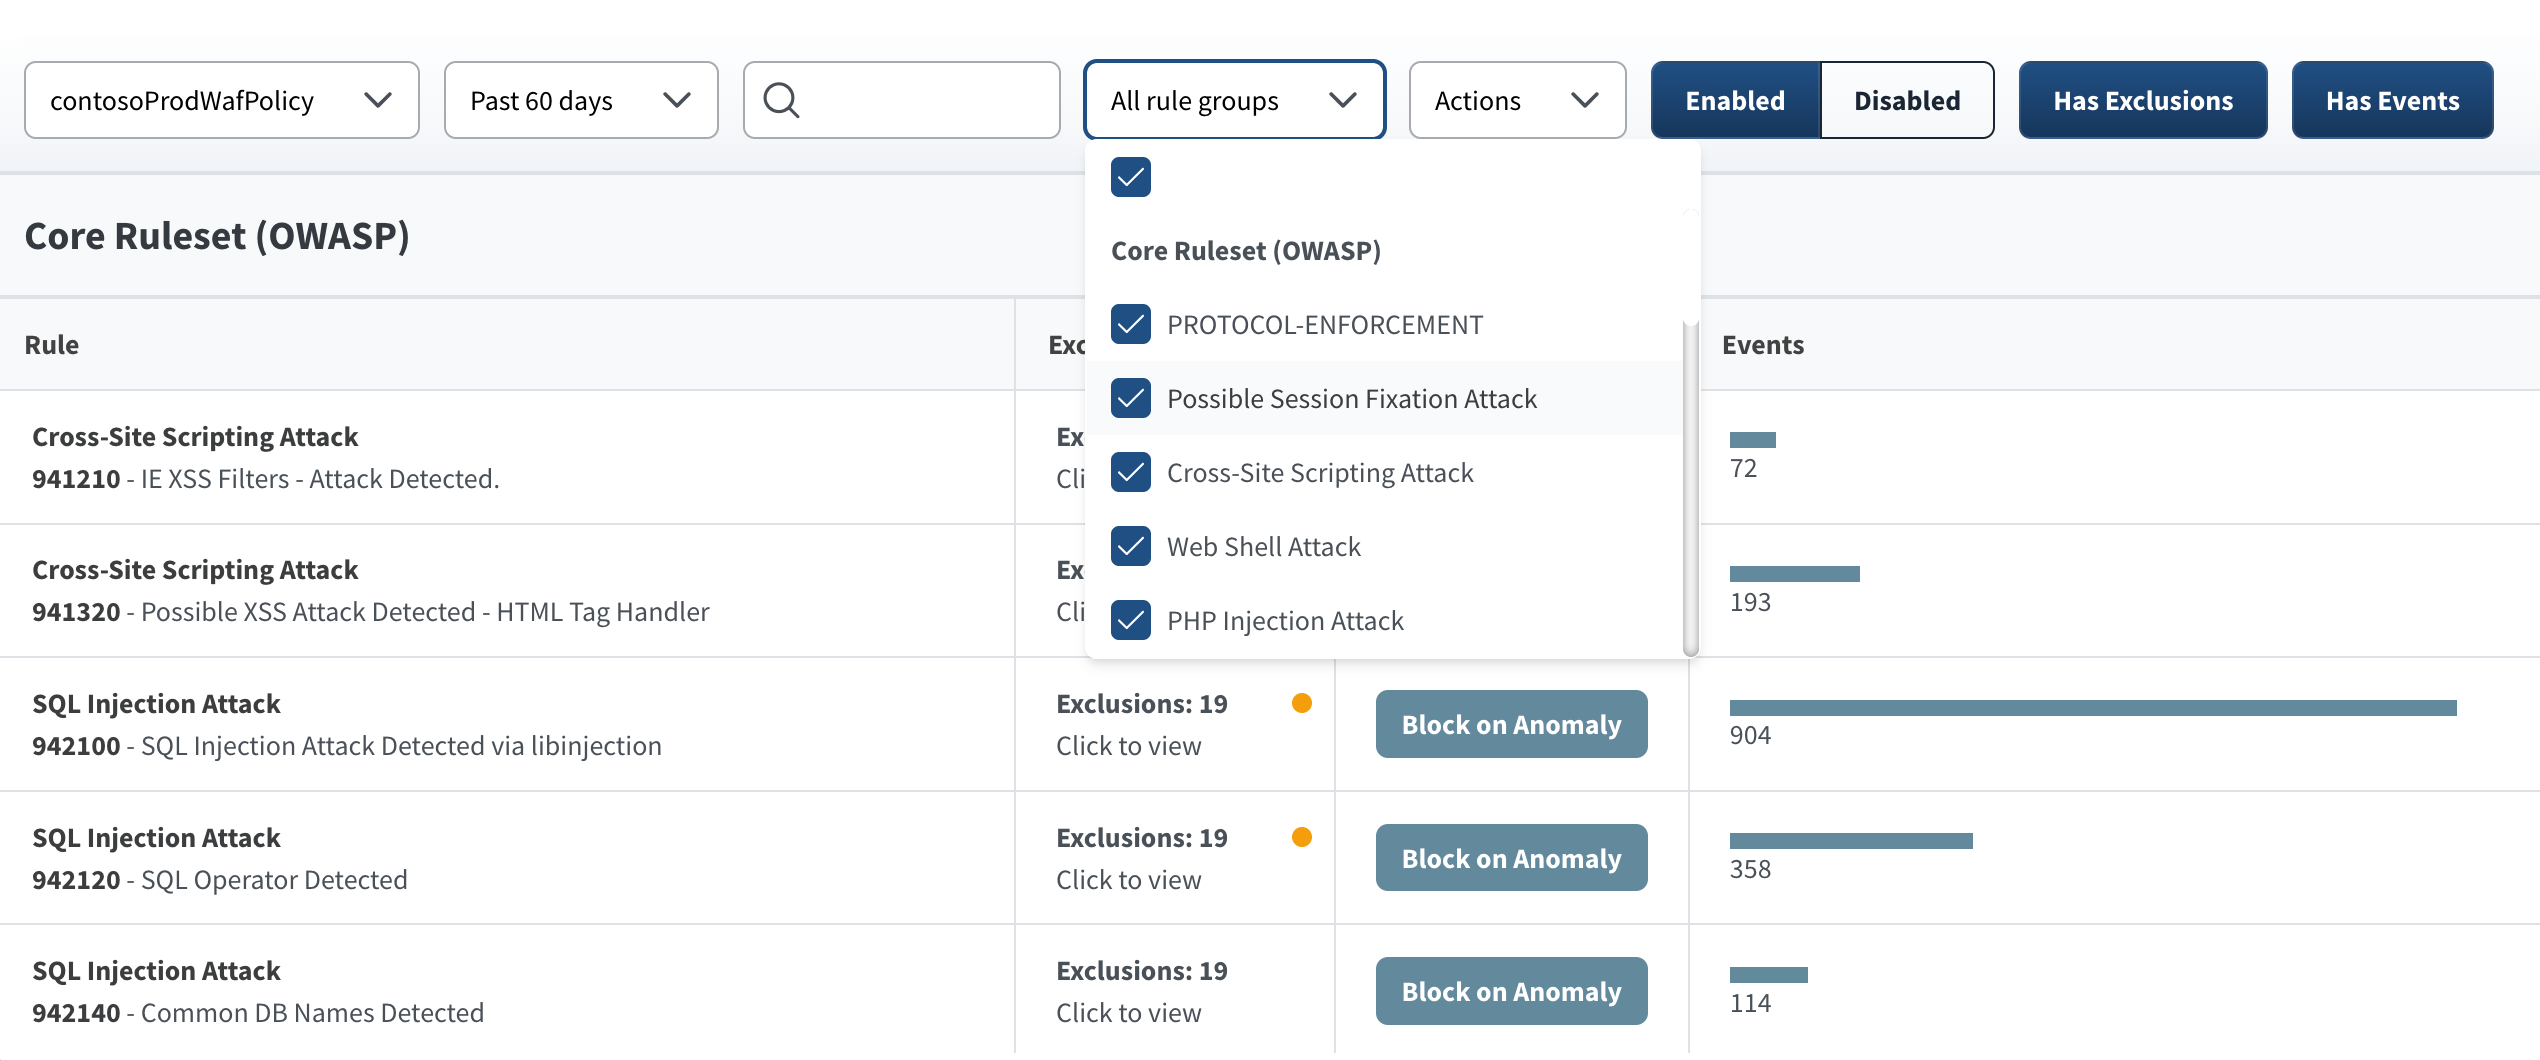
Attack categories covered by OWASP
Beyond OWASP compliant WAF
OWASP core ruleset, matured - per-rule exclusions and anomaly scoring tune it to your traffic.
SQL injection, XSS, RCE and more, covered from day one.
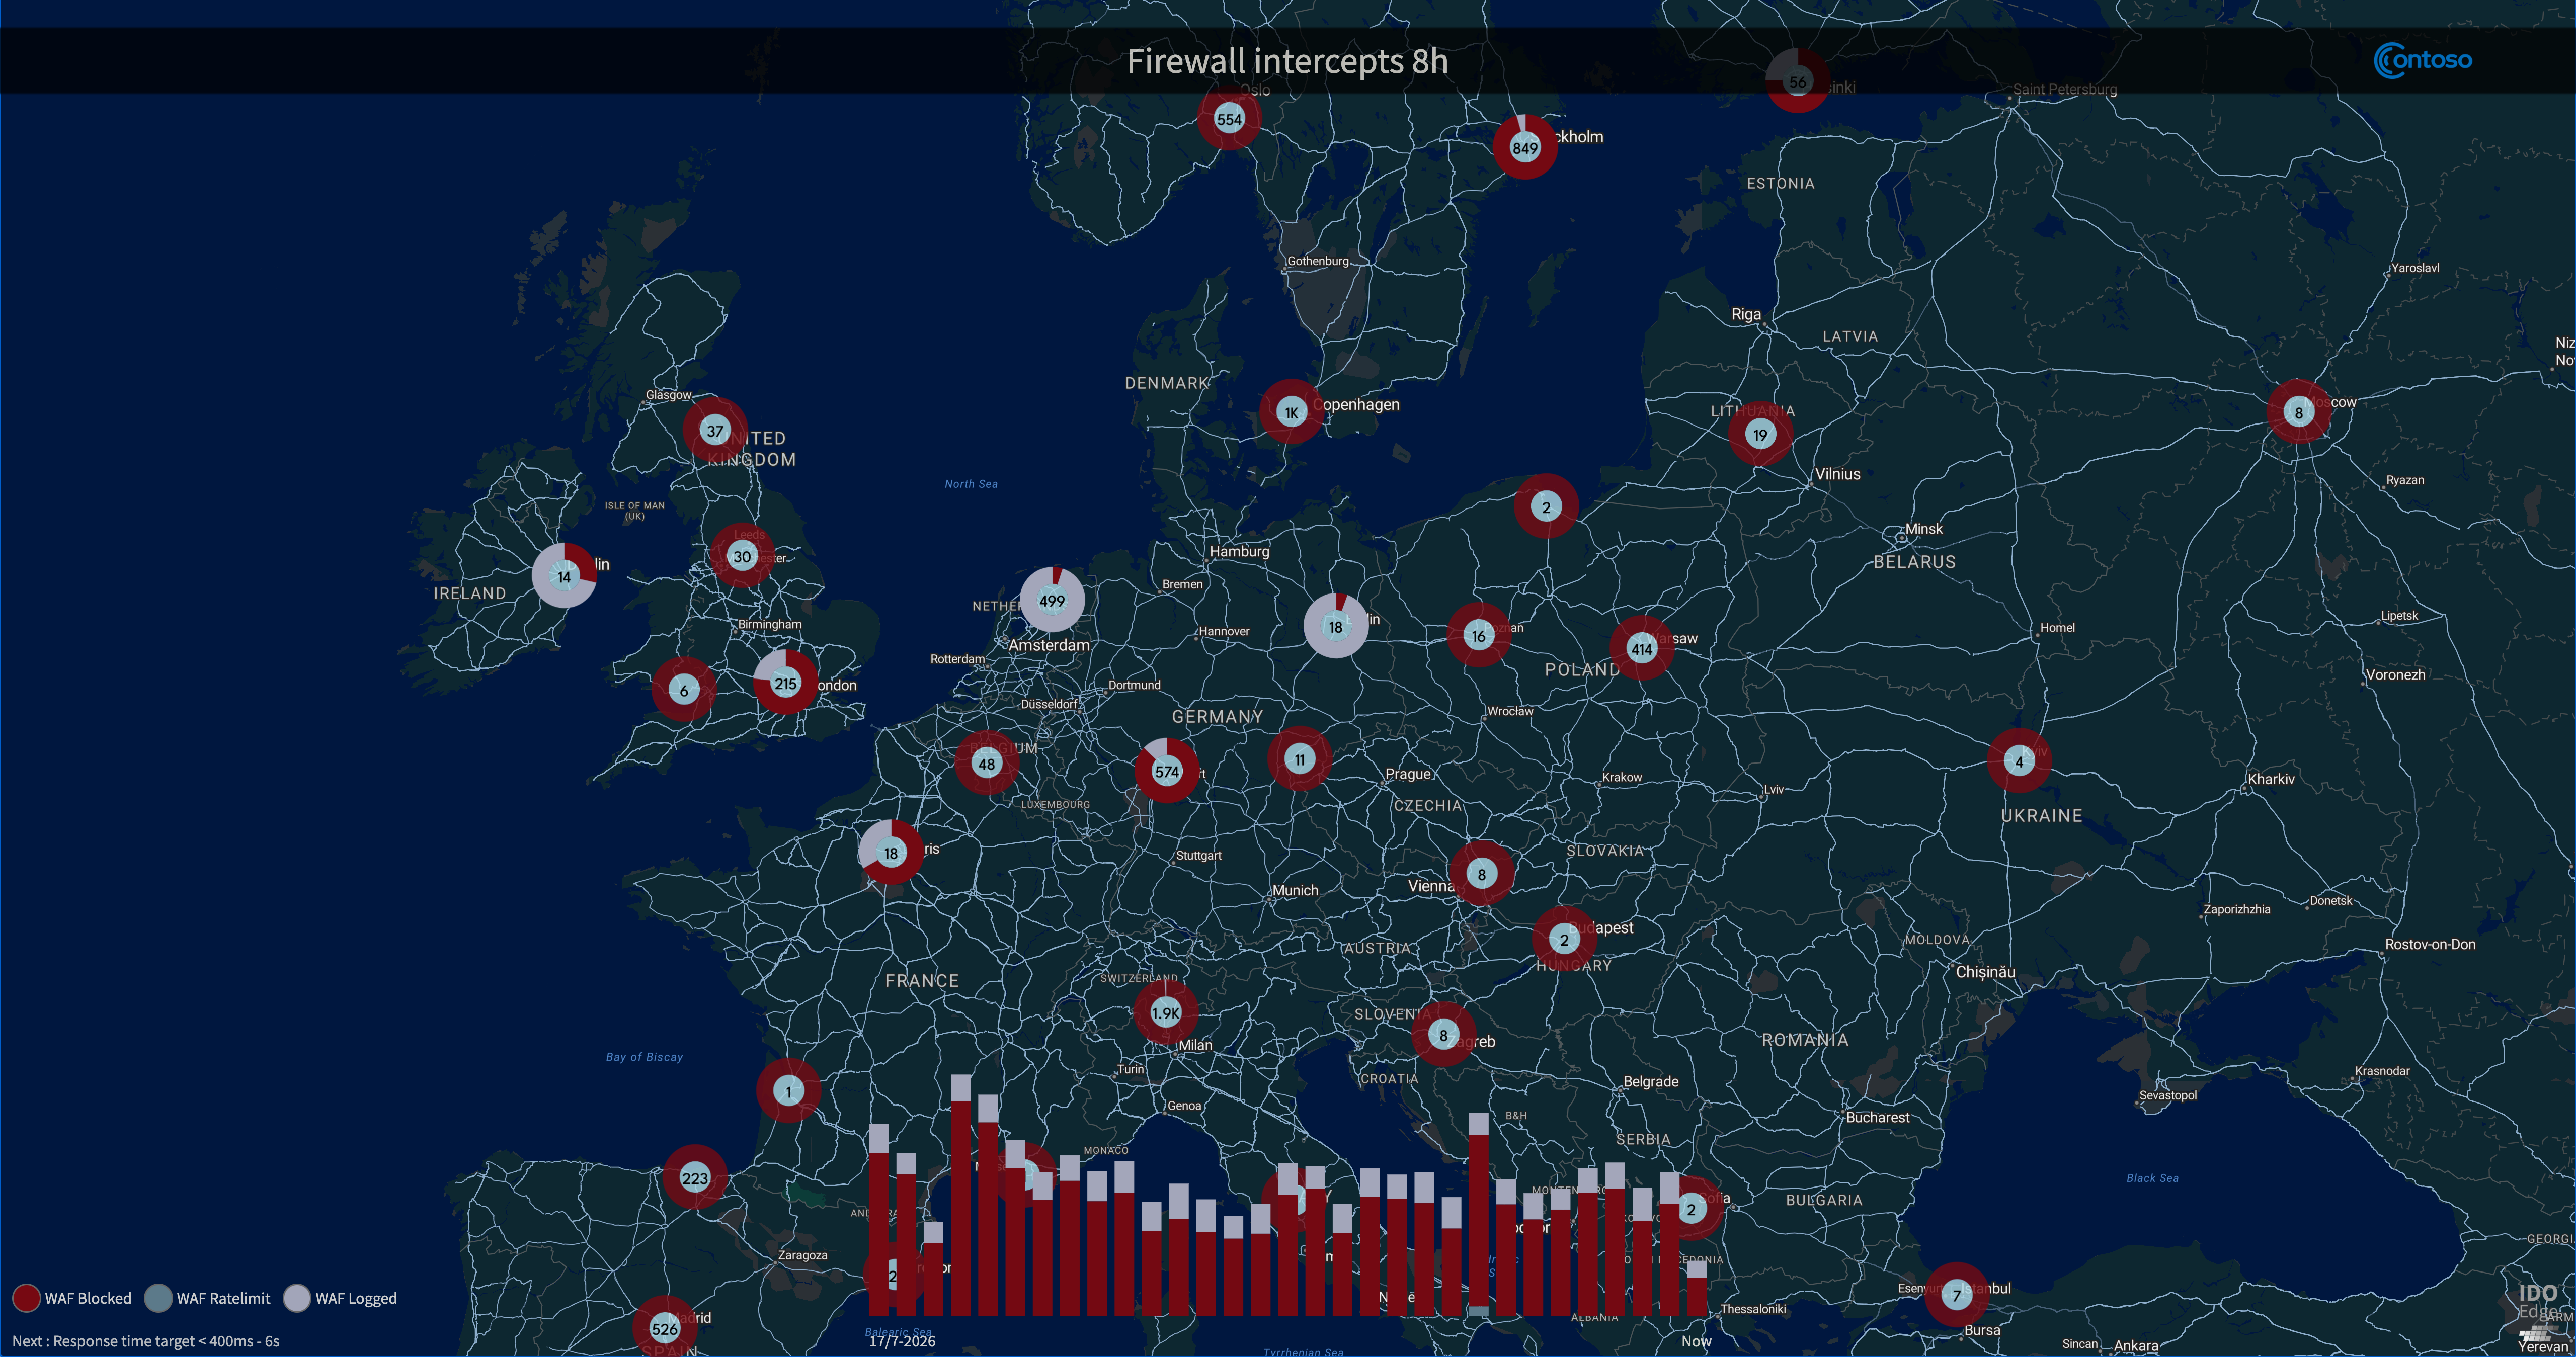
Live security maps
View real-time WAF hits, RADR detections and bot activity on a world map.
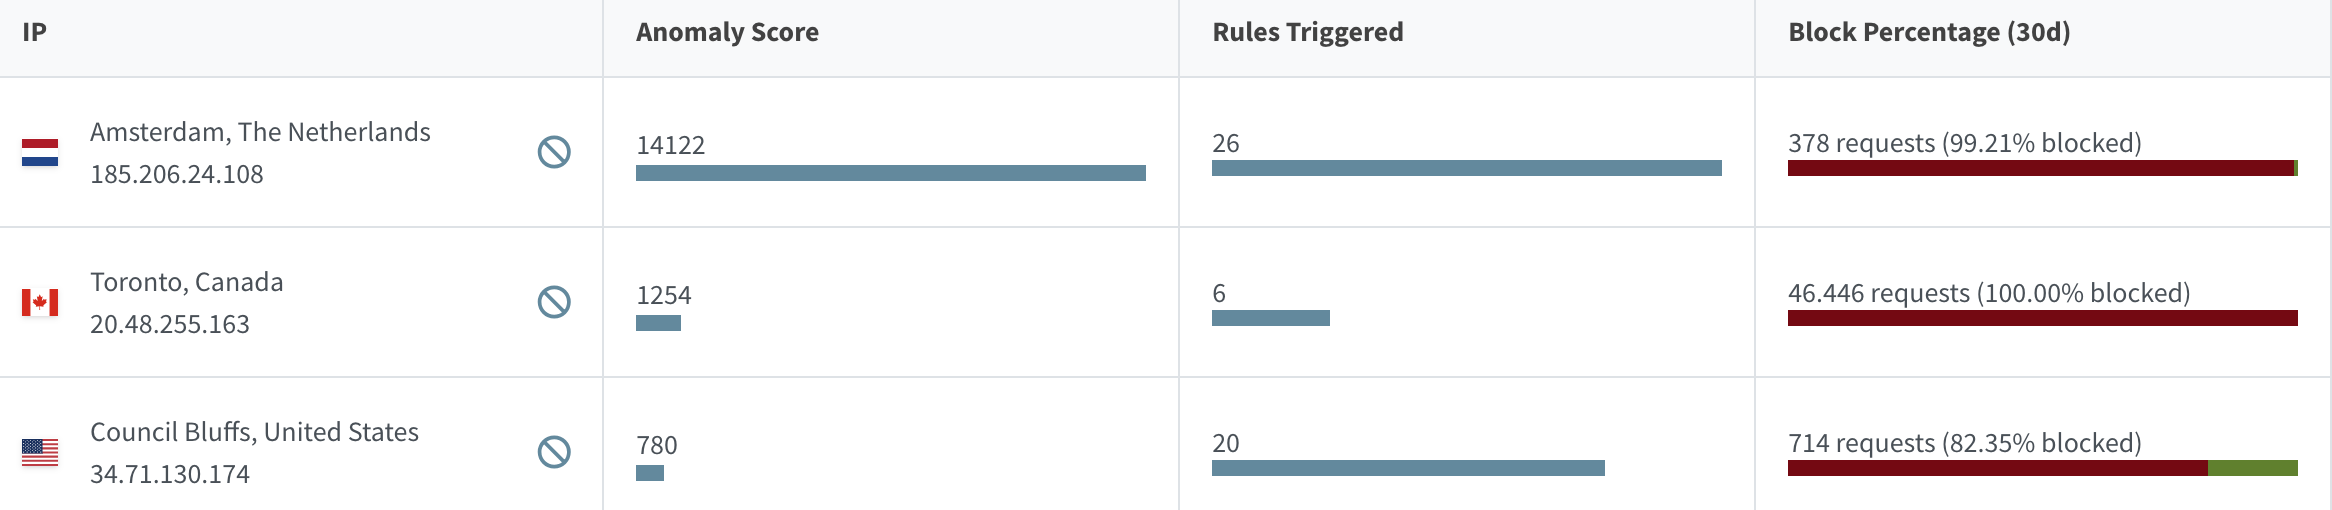
Detection
Anomaly score & rules triggered
Escalation
Block percentage rising
Response
IP blocked at the edge
Meet IDO Edge's apex security feature - RADR
Real-time Attack Detection and Response.
AI-powered attacker profiling, threats identified and escalated within minutes.
Also included
DDoS protection
Always-on mitigation absorbing multi-Gbps attacks at 250+ Points of Presence worldwide
Bot management
Detection and control of credential stuffing, scrapers and fake checkouts
Deep security analytics
Searchable events, full request context, audit-ready logs
Active WAF tuning
Rules mapped to your application's real behaviour, with a minimum of false positives.
Azure-native
100% built on Microsoft Azure, available via Azure Marketplace. Spend counts toward MACC and Enterprise Agreements.
What enterprise web security looks like with IDO Edge
Without IDO Edge
- ✗
Static WAF rules set once and rarely updated - gaps widen as the application changes
- ✗
False positives block legitimate traffic - developers spend time firefighting, not shipping
- ✗
DDoS attacks reach the origin before mitigation kicks in - downtime, degraded performance
- ✗
Bot traffic skews analytics, wastes infrastructure and hides real user patterns
- ✗
Security events invisible to the business - no shared view, no audit trail
With IDO Edge
Managed WAF actively tuned to your application - fewer false positives, stronger coverage over time
RADR detects and flags attackers within minutes - our team responds before the damage is done
DDoS protection absorbs multi-Gbps attacks at the edge - origin stays responsive under load
Bot management filters credential stuffing, scrapers and fake checkouts before they hit your stack
Enterprise web security visible in real time - live dashboards for Security Ops, DevOps and executives
Security experts on the sideline - actively monitoring, tuning and responding on your behalf
Security that protects your users - and your bottom line
RADR detects in real time
Our team responds with tight SLAs, not after the damage is done.
WAF stays effective as your app changes
Active tuning keeps your WAF protection service current with every release.
Faster sites for real users
Removing malicious and bot traffic frees capacity and improves stability and performance.
Lower infrastructure and egress costs
Bad traffic stopped at the edge before it reaches your origin.
Audit-ready security logs
Searchable events with full request context for compliance and incident response.
Enterprise procurement without friction
100% Azure-native, available on Azure Marketplace, counts toward MACC/EAs.
Security built into your Frontend Management suite
Not a separate vendor, contract or dashboard.
How IDO Edge adapts as you change
Getting enterprise web security right isn't a one-time setup. It's an ongoing process - and one IDO Edge manages on your behalf.
Profile
We map your application's real behaviour: cookies, partners, routes and traffic patterns. This baseline is what separates precise protection from blunt rule sets.
Tune
Your WAF protection service is refined to your specific application, minimising false positives and maximising coverage across your entire web estate.
Detect
RADR monitors traffic continuously, identifying attacker behaviour in real time and flagging threats before they escalate.
Respond
Our team acts on detections with tight SLAs. For situations requiring immediate intervention, we escalate and resolve - so your team doesn't have to.
Visualise
Live dashboards give Security Ops, DevOps and leadership a shared, real-time view of attacks, DDoS protection events, bot activity and performance - all in one place.
Reach state-of-the-art security in just four weeks
Most enterprises take months - or never fully get there. IDO Edge's structured four-week onboarding journey changes that. We profile your application, observe real traffic, tune your WAF rules, and deliver a strengthened security posture. By week four, your WAF is calibrated to your specific application, more rules are switched on, and you have a clear picture of every threat hitting your estate.
Find out where your enterprise web security stands today
Most enterprise web security setups have gaps nobody has looked at in months. IDO Edge offers a RADR threat assessment that shows you exactly where you're exposed - before attackers find it first.
Whether you're running a managed WAF that's due for a review, or you're building a security layer from scratch, we'll walk you through what genuine WAF protection service looks like for your specific application.
No lengthy procurement - IDO Edge is available directly on the Azure Marketplace.